
Key Capability
Full control over who sees what, and when
Role-based access, field-level authorization, and full audit logging ensure every system, agent, and person only sees the data they’re permitted to see.
How it works with
The same governance and access control across thousands of integration pairs
Nothing shared by default
Data lands in your Data Lake first, under your control, before anything is exposed to an application, API, or AI model.
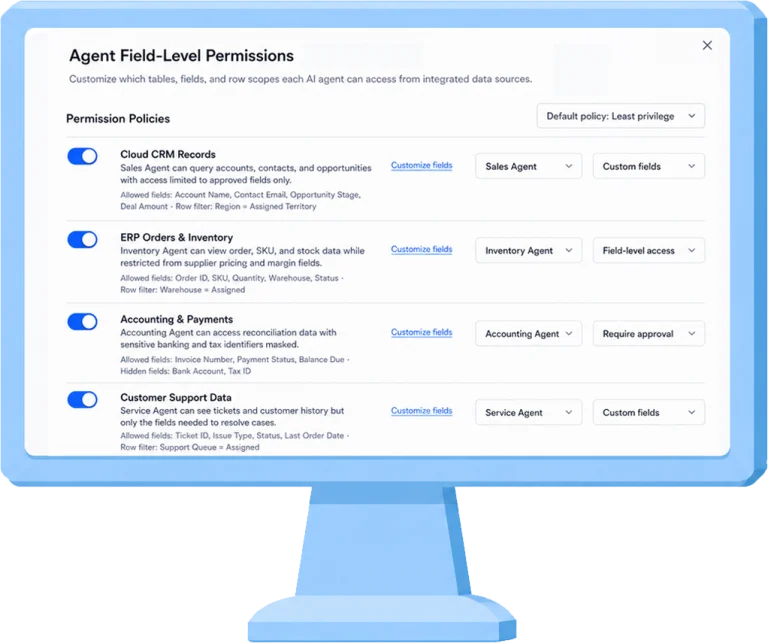
Per-field, per-policy access
You decide exactly what any model or system can see, down to the individual column, rather than granting blanket access to a whole table.
Fully auditable
Every action taken by an agent or integration is logged and traceable, so you can always answer who accessed what, and when.
Frequently asked questions (FAQs)
No, access is governed per field and per policy before any model is granted access.
Access is governed by role and field-level authorization.
Yes, data can be segmented by role, such as sales, support, or accounting.
No. Role-based access, field-level authorization, and audit logging are built into every Commercient implementation, not sold separately.
Permission changes typically go through your administrator(s) or Commercient support, depending on your account configuration.


